
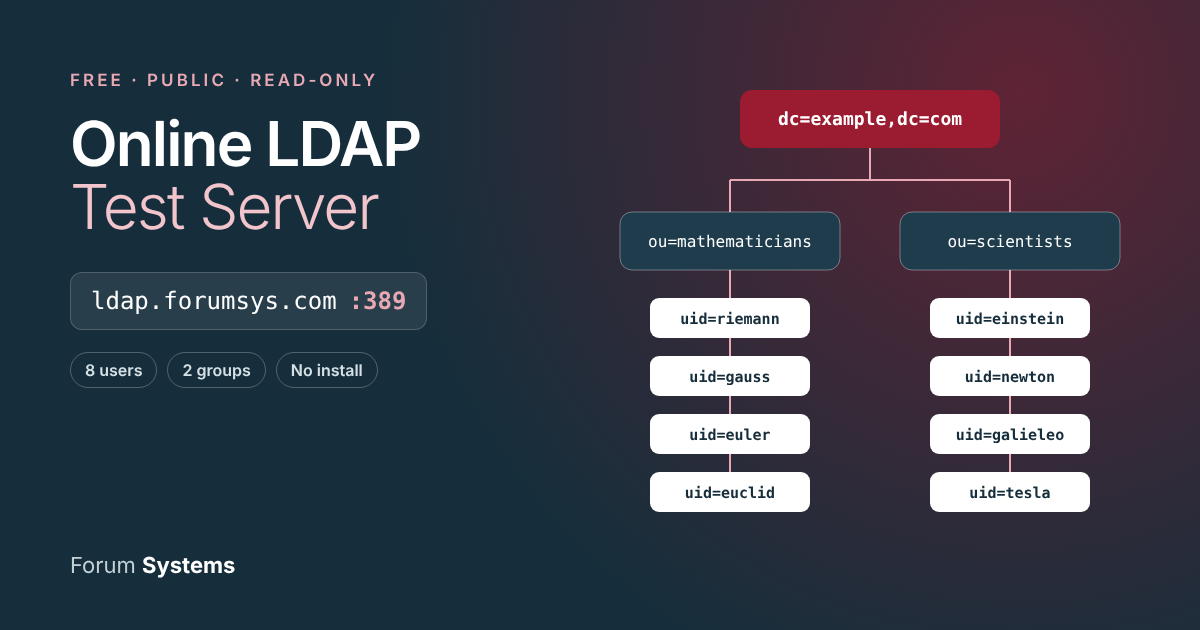
A free, public LDAP directory for testing your application’s LDAP authentication. No download, no install, no configuration: point your app at the server below and start testing connectivity and logins against real identities.
ldap.forumsys.com389dc=example,dc=comcn=read-only-admin,dc=example,dc=compasswordpasswordAll user passwords are password. This is a shared, public test server: never use it with real credentials or production data.
Need this in production? FS Sentry puts LDAP and Active Directory behind SSO, MFA and modern tokens for your APIs and AI agents, with no agents to install.See how →Users and groups
Bind as any individual user (uid) or work with the two groups (ou). Each user’s DN follows the pattern uid=einstein,dc=example,dc=com.
Mathematicians
ou=mathematicians,dc=example,dc=comScientists
ou=scientists,dc=example,dc=com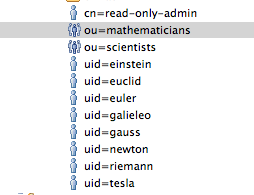
Try it in 30 seconds
Copy any of these to test a search or a login. Every example uses only the details above.
ldapsearch -x -H ldap://ldap.forumsys.com:389 \
  -D "cn=read-only-admin,dc=example,dc=com" -w password \
-b "dc=example,dc=com" "(uid=einstein)"ldapwhoami -x -H ldap://ldap.forumsys.com:389 \
-D "uid=einstein,dc=example,dc=com" -w passwordfrom ldap3 import Server, Connection
server = Server("ldap.forumsys.com", port=389)
conn = Connection(server, "uid=tesla,dc=example,dc=com", "password", auto_bind=True)
conn.search("dc=example,dc=com", "(uid=tesla)", attributes=["cn", "mail"])
print(conn.entries)Hashtable<String, String> env = new Hashtable<>();
env.put(Context.INITIAL_CONTEXT_FACTORY, "com.sun.jndi.ldap.LdapCtxFactory");
env.put(Context.PROVIDER_URL, "ldap://ldap.forumsys.com:389");
env.put(Context.SECURITY_AUTHENTICATION, "simple");
env.put(Context.SECURITY_PRINCIPAL, "uid=newton,dc=example,dc=com");
env.put(Context.SECURITY_CREDENTIALS, "password");
DirContext ctx = new InitialDirContext(env); // throws if the bind failsvar entry = new DirectoryEntry(
"LDAP://ldap.forumsys.com:389/dc=example,dc=com",
"uid=gauss,dc=example,dc=com",
"password",
AuthenticationTypes.None);
object native = entry.NativeObject; // throws if the bind failsPrefer a visual tool? Apache Directory Studio is a good choice for browsing this directory, and for searching, editing and maintaining your own LDAP server.
Common gotchas
FROM TEST TO PRODUCTION
Testing LDAP today? Production identity is harder.
Real environments mix LDAP and Active Directory with Okta, SAML, OAuth and JWT, across legacy apps, cloud services, partners and now AI agents. FS Sentry connects to your directories and converts any identity into the token each application expects, with SSO, multi-factor authentication and no agents to install.
Frequently asked questions
Is the online LDAP test server free?
Yes. Forum Systems provides it free for testing connectivity and authentication, so you don’t have to download, install and configure your own LDAP server.
Can I add or change users?
No. Access is read-only. You can search and bind as the users and groups listed on this page.
What is the password for the test users?
Every user, and the read-only admin, uses the password: password.
Why does my bind fail?
Check the DN format (uid=einstein,dc=example,dc=com), the port (389), the spelling of galieleo, and whether your network allows outbound LDAP. In .NET, use LDAP:// in uppercase.
What tool do you recommend for browsing the directory?
Apache Directory Studio works well for connecting to this server and for maintaining your own.
How do I use LDAP for SSO across APIs, cloud apps and AI agents?
FS Sentry connects to LDAP, Active Directory, Okta and other identity providers, and converts identities into SAML, OAuth, JWT and other tokens, with MFA and no agents to install.